
What ADAS Supplier Documents Are Needed for Vehicle Approval?
A vehicle approval package for an ADAS function is not a single certificate or a stack of generic quality files. It is a connected set of evidence showing what the system does, how it was developed, how it behaves when conditions degrade, and how the supplier controls changes after production begins.
For teams asking, “What ADAS supplier documents are needed for vehicle approval?”, the practical answer is: provide documentation across the product definition, safety case, software verification, cybersecurity, vehicle-level validation, production traceability, and change-management process. The OEM or approval authority must be able to follow the evidence from the sensor and electronic control unit through the vehicle function and its driver-facing behavior.
A camera supplier, radar supplier, domain-controller provider, software developer, and system integrator will not own the same documents. What matters is that ownership is clear and that the files fit together without gaps or conflicting assumptions.
Start with the approval scope, not a generic document checklist
Before requesting documents from an ADAS supplier, define the feature being approved. “Front camera” is a component description; “lane-keeping assistance” or “automatic emergency braking” is a vehicle function. Approval evidence is usually judged at the function level, even when much of the technical evidence comes from individual suppliers.
The required package changes with the function’s operational design domain. A parking assist feature, highway driving support function, driver monitoring system, and blind-spot warning system face different failure modes, user expectations, sensor limitations, and interface dependencies. A document set that is adequate for a warning-only feature may be insufficient for a system that applies steering or braking.
The first useful document is therefore a scope and responsibility matrix. It should identify:
- the vehicle function and intended operating conditions;
- the supplied hardware, embedded software, calibration data, and cloud-connected elements;
- interfaces with braking, steering, power supply, instrument displays, data networks, and driver controls;
- which organization owns system integration, vehicle testing, regulatory submission, and field monitoring;
- which supplier assumptions must be maintained by the vehicle manufacturer.
This prevents a common approval failure: each supplier submits credible component-level reports, but no party demonstrates that the final vehicle behaves safely when those components interact.
Core ADAS supplier documents for vehicle approval
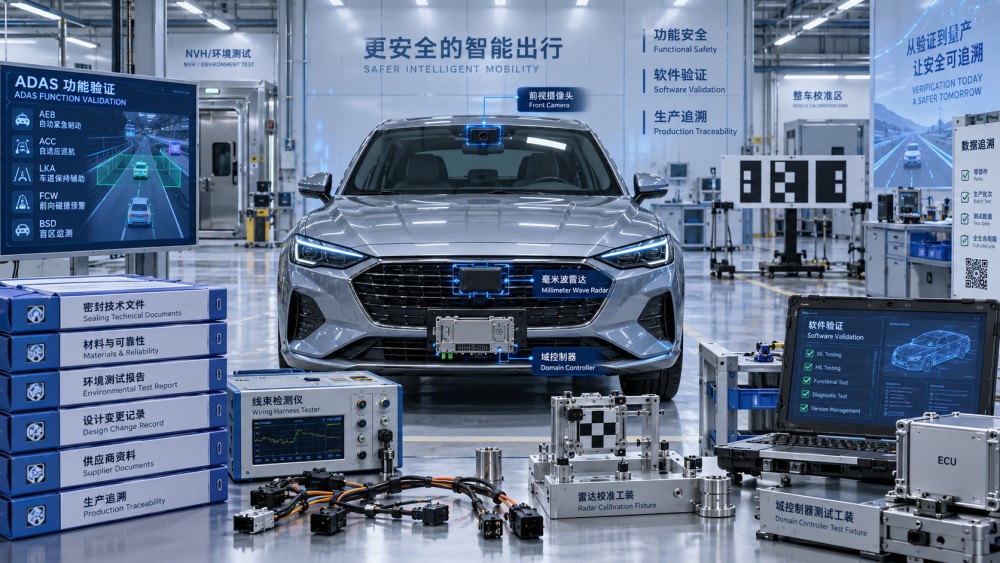
What belongs in the technical product file?
The technical file is the reference point for the whole approval package. It should identify the delivered configuration precisely enough that a reviewer can distinguish a tested production release from a later engineering sample.
At a minimum, it should cover the sensor or controller architecture, wiring and network interfaces, communication protocols, diagnostic functions, calibration dependencies, physical installation constraints, and relevant environmental limits. For perception sensors, include limitations caused by placement, field of view, occlusion, contamination, lighting, weather, reflectivity, or sensor alignment where these affect the stated function.
Do not treat a supplier datasheet as a complete technical file. Datasheets usually describe capability. Approval needs the conditions under which that capability is valid. For example, a perception component may detect an object in a controlled test, while the vehicle-level feature still depends on mounting position, windshield characteristics, bumper material, cleaning strategy, braking response, display logic, and driver warnings.
Why functional safety files need assumptions of use
Functional safety documentation is often requested early, but it becomes useful only when it is tied to the vehicle architecture. A supplier safety case should not simply state that the component has safety mechanisms. It should explain the faults considered, the resulting risks, how faults are detected, what response is expected, and what conditions the integrator must provide.
Those conditions are commonly called assumptions of use. They may include reliable power supply behavior, watchdog supervision, valid vehicle-speed input, a defined braking-system response, display availability, network timing, or diagnostic handling. The OEM needs to evaluate whether these assumptions are actually met in the target vehicle.
A frequent mistake is to file the supplier’s safety manual without converting its assumptions into vehicle requirements and verification activities. That leaves an apparent safety document trail but no proof that the vehicle integration honors it.
Safety evidence should include the degraded state
ADAS approval is not only about correct operation in favorable conditions. The documentation must describe what happens when a camera is obscured, radar data becomes implausible, a communication message is delayed, a processor resets, a calibration value is invalid, or the system reaches an operating limit.
The expected response may be a warning, a controlled function withdrawal, a fallback mode, or a fault indication. The appropriate response depends on the function and vehicle design. The important point is consistency: the requirement, safety concept, user information, diagnostic behavior, and test report should describe the same response.
Software validation must be release-specific
ADAS approval packages often become weak at the software boundary. Teams may have extensive test material, yet cannot show which exact software build, parameter set, machine-learning model, or calibration was installed on the test vehicle. That creates uncertainty about whether the evidence applies to the production release.
Supplier documentation should therefore include a controlled software release record. It should identify version numbers, compatible hardware, included functions, known restrictions, test status, and the approval status of any open anomalies. Where behavior is influenced by configurable thresholds or vehicle variants, the configuration should be traceable as well.
For software that is updated after sale, the package also needs a controlled change process. A supplier should be able to explain how it assesses whether an update affects safety, cybersecurity, performance, driver information, calibration, or prior approval evidence. An update that seems minor at code level can alter braking timing, alert behavior, object classification, or diagnostic coverage at vehicle level.
Cybersecurity documents are part of the approval story
Cybersecurity evidence should be proportional to the component’s exposure and influence. A non-connected sensor still has interfaces that could affect vehicle behavior. A connected ADAS controller, telematics-linked feature, or remote-update path requires a more extensive package because threats can emerge after production.
Useful supplier records include threat analysis, security requirements, access-control design, secure boot or software-integrity measures where applicable, key and credential management, vulnerability handling, and a process for communicating security-relevant changes to the vehicle manufacturer. The focus should be on demonstrable lifecycle control, not on a one-time statement that a product is “secure.”
Test reports need context, not just pass/fail conclusions
Test reports carry the most weight when they make their boundaries visible. A credible ADAS report identifies the item tested, software and calibration versions, test method, instrumentation, relevant environmental conditions, acceptance criteria, deviations, and the result. A summary slide stating “passed” does not allow a reviewer to judge applicability.
The complete validation plan normally combines several evidence types. Simulation and software testing are useful for broad scenario coverage. Bench and hardware-in-the-loop testing help expose interface and diagnostic faults. Vehicle testing confirms that installation, control response, warnings, and real-world signals work together. Environmental, electrical, and electromagnetic compatibility evidence helps establish that the hardware remains dependable under expected vehicle conditions.
Coverage should follow the function’s risks. For a forward-looking intervention function, interactions with braking, driver override, target loss, sensor blockage, and warning timing may be more relevant than an isolated object-detection metric. For cabin-facing monitoring, occlusion, occupant variation, lighting changes, privacy-related data handling, and driver notification logic may require closer attention.
Production evidence protects the link between approval and serial vehicles
Vehicle approval is undermined if the tested configuration cannot be reproduced in production. Suppliers should provide evidence of configuration control, production release criteria, end-of-line testing, traceability, handling of nonconforming parts, and management of sub-tier suppliers. The detail required will vary by component, but the principle remains the same: the delivered unit needs a known relationship to the unit that generated the validation evidence.
This is particularly important for sensors with alignment-sensitive installation, controllers with multiple software variants, and systems dependent on calibrated parameters. A well-designed end-of-line process may confirm identity, communication, diagnostics, and calibration status, but it does not replace vehicle-level validation after a vehicle architecture change.
How to assemble the package without creating rework
The most efficient approach is to build an evidence map before the final vehicle test phase. List each vehicle requirement, the responsible party, the relevant document, the configuration covered, and the test or review that closes the requirement. This exposes missing interfaces early.
- Freeze a preliminary function definition and supplier responsibility split.
- Collect supplier safety manuals, interface specifications, software-release rules, and cybersecurity responsibilities before detailed integration is complete.
- Turn supplier assumptions into vehicle-level requirements with named owners.
- Plan validation around normal operation, misuse reasonably foreseeable for the function, and degraded conditions.
- Lock the tested hardware, software, calibration, and vehicle configuration into a release baseline.
- Review every late design change against the affected approval evidence.
For organizations tracking both perception systems and cabin safety components, this evidence discipline should extend beyond ADAS electronics. GNCS follows the relationship between precision spatial perception, occupant protection, body structures, seat systems, and regulatory evidence because vehicle safety functions rarely stand alone. An ADAS warning may depend on the instrument panel and seat behavior; an intervention may depend on brakes, body-network integrity, and driver restraint or seating context. Approval documentation is stronger when these dependencies are treated as engineering interfaces rather than separate supplier workstreams.
Common documentation gaps that delay approval
Using component evidence as proof of vehicle performance. A supplier can validate its own item thoroughly, but the final function may change with installation geometry, vehicle dynamics, display behavior, and actuator response.
Missing version control. Reports without a clear hardware, software, and calibration baseline become difficult to use after even a small release change.
Unowned supplier assumptions. Safety manuals and integration guides often contain conditions that neither the OEM nor the Tier 1 has formally verified.
Separating cybersecurity from functional behavior. A cybersecurity event can affect availability, integrity, diagnostics, or update status. It should be considered alongside the vehicle’s safe response.
Testing only the intended use case. Approval evidence must also show how the function limits, warns, disengages, or recovers when inputs are unreliable or operating conditions fall outside its defined range.
FAQ
Does every ADAS supplier need to submit the full vehicle approval file?
No. Each supplier should provide evidence for the item and responsibilities it controls. The vehicle manufacturer or system integrator normally combines that evidence with vehicle-level requirements, integration results, and the final approval submission.
Are quality-management documents enough for ADAS approval?
No. Quality records support production consistency, but they do not prove functional behavior, safe fault handling, software validity, cybersecurity control, or performance in the installed vehicle.
Can simulation replace vehicle testing?
Simulation is valuable for repeatable and difficult scenarios, but it cannot by itself establish the complete behavior of the installed vehicle. Physical integration, sensor placement, actuator response, human-machine interface behavior, and environmental effects still require appropriate vehicle-level evidence.
What should be reviewed when an ADAS software update is released?
Review the affected requirements, safety assumptions, cybersecurity controls, calibration compatibility, test coverage, open defects, user-facing behavior, and any evidence used for the approved vehicle configuration. The review should determine whether existing validation remains applicable or needs to be supplemented.
Related News

How to Evaluate Supplier Solution References Before Signing a Contract
Evaluate supplier solution references with confidence. Learn how to verify technical evidence, identify delivery risks, and close gaps before signing a contract.

How Capacitive Seat Occupancy Sensing Works in Automotive Airbag Systems
Discover how capacitive seat occupancy sensing supports automotive airbag systems, and explore the design, calibration, and validation challenges behind reliable performance.

Industrial Product References: How to Verify Specs Before Ordering
Use an industrial product reference for procurement to verify specs, compatibility, and certifications before ordering—and reduce costly purchasing risks.

Choosing a Private Label Partner in Europe: Key Supplier Criteria
Private label cooperation Europe buyers can trust starts with the right supplier. Explore key criteria for compliance, quality, traceability and supply resilience.

Integrated Cabin Comfort Systems: How Seat and Cabin Climate Controls Work Together
Discover how integrated cabin comfort systems coordinate seat and climate controls to balance occupant comfort, energy use, safety, and performance.

Automotive Ergonomics Pricing: What Drives Seat System Costs?
Discover what drives automotive ergonomics pricing, from seat mechanisms and safety systems to tooling and volume, and learn how to compare supplier quotes.

Evaluating Supplier Solutions: How to Verify References and Standards
Supplier solution references and standards can make or break a sourcing decision. Learn how to verify claims, assess compliance, and reduce risk before awarding a contract.

Choosing B2B Product Knowledge Platform Suppliers: Key Evaluation Criteria
Compare B2B product knowledge platform suppliers with confidence. Explore key criteria for data accuracy, supplier transparency, integrations, and value.

Choosing a Marine Radar Systems Supplier: What to Check Before Buying
Choosing a marine radar systems supplier? Compare installed costs, bridge compatibility, compliance evidence, and service support before you buy.
Related News
- 00
0000-00
How to Evaluate Supplier Solution References Before Signing a Contract - 00
0000-00
Industrial Product References: How to Verify Specs Before Ordering - 00
0000-00
Choosing a Private Label Partner in Europe: Key Supplier Criteria - 00
0000-00
Automotive Ergonomics Pricing: What Drives Seat System Costs? - 00
0000-00
Evaluating Supplier Solutions: How to Verify References and Standards
0000-00
Weekly Insights
Stay ahead with our curated technology reports delivered every Monday.